S&J Corporation has expanded the monitoring scope of its “My SOC 365” security monitoring service to include Microsoft Azure and Microsoft Purview. The background behind this move is that, with the adoption of cloud computing, the IT environments that companies must protect have rapidly expanded, increasing the need to centrally monitor external attacks and internal threats.
- Key Event: Launch of 24/7 monitoring for Microsoft Azure and Microsoft Purview
- Securing Cloud Infrastructure: Early Detection of Suspicious Access via Microsoft Azure Integration
- Preventing Information Asset Leaks: Monitoring and Detection of Insider Threats Based on Microsoft Purview
- Security Report Enhancement: Identifying Organizational Weaknesses and Shadow IT Through Weekly Visualization
- Agentless Deployment: Maximizing Existing Environments by Eliminating Endpoint Operations
- Future Outlook and Key Points: Expansion of Automated Remediation and Compliance Policy for the SCS Evaluation System
Key Event: Launch of 24/7 monitoring for Microsoft Azure and Microsoft Purview
On September 1, 2026, S&J Corporation (TSE Growth: 5599), a cybersecurity company, launched an enhanced version of its “My SOC 365 Service”—which maximizes the use of Microsoft 365 as an integrated security platform—that newly adds Microsoft Azure and Microsoft Purview to its monitoring targets. In recent years, as corporate cloud adoption has rapidly progressed, the IT environment that needs to be protected has expanded beyond traditional devices and accounts. Amid strong demands not only to monitor for external cyberattacks, but also for internal fraud abusing legitimate privileges, the company has established a 24/7 monitoring system under a single framework that covers attacks on cloud infrastructure and the exfiltration of information assets, in addition to conventional monitoring targets such as accounts, devices, emails, and cloud apps. This enhancement realizes an integrated security monitoring model that comprehensively covers everything from entry points to cloud infrastructure and critical data, enabling robust corporate defense.
Securing Cloud Infrastructure: Early Detection of Suspicious Access via Microsoft Azure Integration
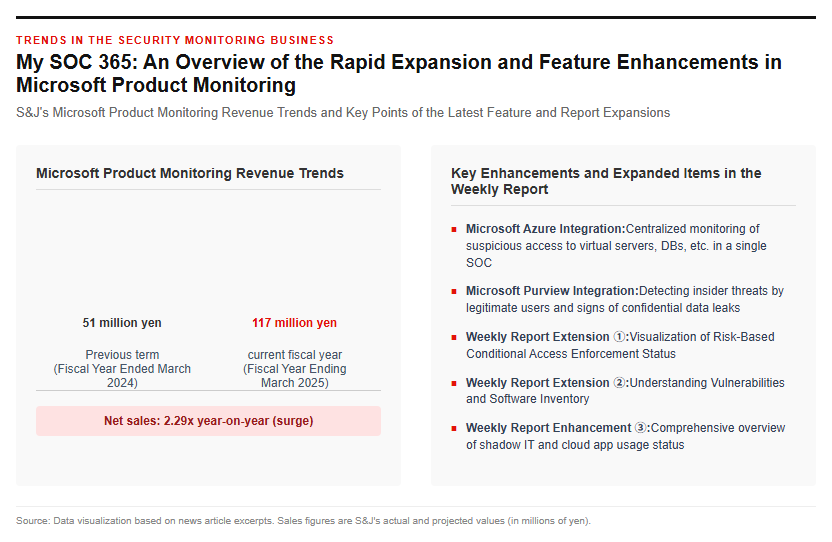
By adding support for Microsoft Azure monitoring, it has become possible to quickly detect a sequence of behaviors such as attacks on virtual servers, containers, storage, and databases in the cloud, as well as the abuse of credentials and suspicious access. Generally, when Microsoft 365 and cloud infrastructure are monitored by separate services or monitoring providers, delays tend to occur in information sharing and situational judgment when critical alerts are generated, posing a risk of expanding damage. However, this functional enhancement enables centralized monitoring under a single SOC (Security Operations Center) structure, making it possible to detect the spread of attacks early and eliminate bottlenecks in coordination between providers. S&J is rapidly expanding its monitoring track record in this field, with Microsoft product monitoring sales for the fiscal year ending March 2025 surging to 117 million yen from 51 million yen in the previous fiscal year. Please note that using Azure monitoring requires a separate application and the activation of Microsoft Defender for Cloud.
Preventing Information Asset Leaks: Monitoring and Detection of Insider Threats Based on Microsoft Purview
Another key pillar of this enhancement is the integration with Microsoft Purview, which monitors and manages an enterprise’s entire data assets. This enables the automatic detection of suspicious activities—such as the external sharing or transmission of confidential information, the downloading of a large volume of files in a short period, and various file operations that violate policies—based on security policies predefined by customers. In recent years, the intentional removal of information by employees with legitimate privileges and the accidental leakage of confidential information have become serious management challenges, but such signs of internal threats cannot be fully captured through conventional device monitoring alone. With My SOC 365, alongside monitoring for sophisticated external cyberattacks, organizations can now detect signs of internal misuse by authorized users within the same operational monitoring framework, powerfully supporting a system that reliably protects confidential data, which is a company’s most critical asset.
Report Expansion and Ease of Deployment Supporting Corporate Security Visualization
Security Report Enhancement: Identifying Organizational Weaknesses and Shadow IT Through Weekly Visualization
Along with this feature enhancement, the items included in the weekly security reports provided to customers have been significantly expanded. The newly added items are targeted at Microsoft 365 E7 or E5 subscribers, and specifically, the following four items will now be included in the report.
- Risk-Based Conditional Access Implementation Status
- Vulnerability
- Software Inventory
- Shadow IT and Cloud App Usage Status
This makes it possible not only to report on the status of responses to threats that have already occurred and been detected, but also to fully visualize system vulnerabilities still lingering within the organization, and even unauthorized cloud service usage by employees that the IT department is unaware of. It provides extremely effective decision-making material for understanding the current state of a company’s security measures based on objective data and optimizing future security investments. Please refer to the figure below for an example of what the visualization in the weekly report looks like.
Agentless Deployment: Maximizing Existing Environments by Eliminating Endpoint Operations
One of the major technical strengths of My SOC 365 is its agentless operation. Even with this expansion of the monitoring scope to Microsoft Azure and Microsoft Purview, there is no need for any complex deployment tasks, such as installing special software on user devices or rebuilding the monitoring environment. By simply making changes such as log settings in the existing Microsoft 365 environment, users can smoothly transition to an advanced, integrated monitoring system. Even for small and medium-sized enterprises that find it difficult to secure dedicated in-house security personnel, the service maintains the simplicity of launching an advanced monitoring regime in as short a period as 5 days, while minimizing business disruption and implementation costs. The high practicality of incorporating a cutting-edge defense system without increasing operational burdens, while maximizing the effectiveness of existing security investments, is the defining characteristic of this service.
Future Outlook and Key Points: Expansion of Automated Remediation and Compliance Policy for the SCS Evaluation System
S&J Corporation has announced plans to continue enhancing the features of My SOC 365. Already on August 3, 2026, it added an automated response function where AI automatically evaluates threats and executes account disablement or device isolation within tens of seconds of detection, but in October 2026, it plans to expand the scope of this automated response from conventional cloud accounts to internal Active Directory accounts. This will enable simultaneous account containment across both cloud and internal networks. Furthermore, in November 2026, the provided security reports are scheduled to be adapted so that customers can use them as-is as evidence for the “Security Measure Evaluation System for Strengthening Supply Chains (SCS Evaluation System)” operated by the Information-technology Promotion Agency (IPA). This is expected to significantly reduce the audit burden on companies that are required by business partners to disclose their security measures.
Reference Page
- [My SOC 365 Service | S&J Co., Ltd.] https://www.sandj.co.jp/services/mysoc365/
- [Security Measures Evaluation System for Strengthening Supply Chains (SCS Evaluation System) | IPA] https://www.ipa.go.jp/security/scs/index.html
【#Cybersecurity #CloudSecurity #Microsoft_Azure #S&J #DataLeakPrevention #SCSEvaluationSystem #My_SOC_365】
コメント