Assured, Inc. has begun offering an answer search function that enables cross-sectional verification of the security measure status for each cloud service in use. This initiative addresses the urgent challenge for adopting companies to advance their supply chain management, given that approximately 20% of cyberattack damages are related to cloud services.
- Background and Key Points of the New “Answer Search” Feature Launch
- The Surge in Incidents and the Frontline Challenges of Individual Investigations
- The Role Played by the Security Assessment Platform “Assured”
- Inspection Mechanism via Question/Keyword Search and Expert Recommendations
- Practices for Rapid Response in Emergencies and Strengthening Governance in Peacetime
- The wave of regulation and standardization, such as financial guidelines and SCS evaluation systems
- Future Outlook and Key Focus Areas for Cloud Risk Visualization
Background and Key Points of the New “Answer Search” Feature Launch
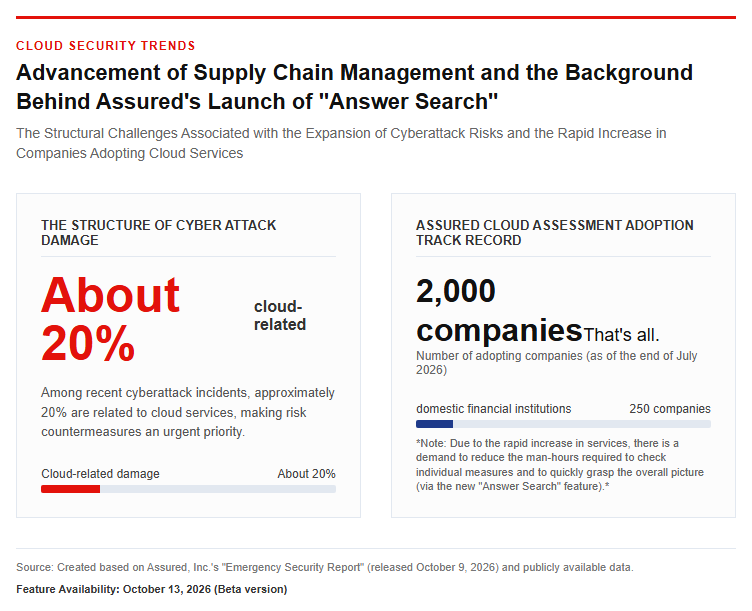
On October 13, 2026, Assured, Inc., which drives the cybersecurity business for the Visional Group, launched a new feature—Answer Search (Beta)—on Assured Cloud Assessment, its cloud security assessment platform. This feature enables users to cross-check and compare vendors’ response contents question by question for cloud services such as SaaS that have completed assessments on the platform. The feature is available to all subscribing companies of both the Standard and Financial editions. As of the end of July 2026, the number of adopting companies has reached over 2,000, including 250 financial institutions. According to an urgent security report released by Assured on October 9, 2026, approximately 20% of recent cyber attack damages were incidents related to cloud services. With the rapid surge in adopted services, the risk of incidents is growing for both user companies and vendors alike. The primary background for this development was the demand to build an advanced governance environment capable of swiftly grasping the overall picture while significantly reducing the massive man-hours required to verify individual security measures.
The Surge in Incidents and the Frontline Challenges of Individual Investigations
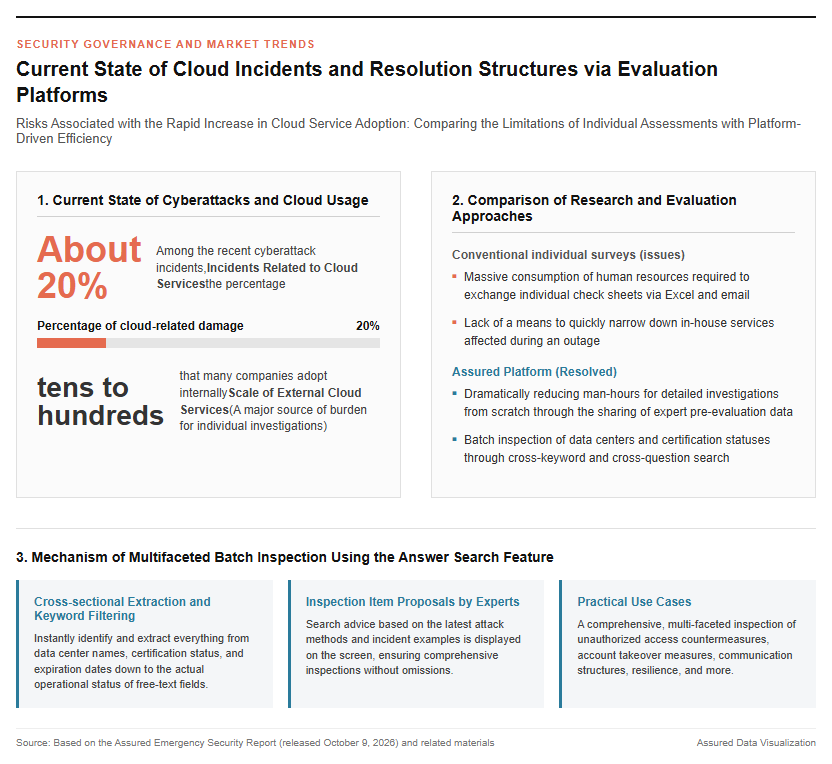
While digital transformation accelerates in many companies, security incidents via the cloud services they use and external contractors have become a serious social problem. As companies adopt dozens to hundreds of external cloud services internally, the task of individually investigating and evaluating the safety and operational status of each provider has imposed a heavy burden on information systems departments and security personnel. In conventional operations, the mainstream practice has been to exchange proprietary security checklists via email or in Excel format, consuming vast amounts of time and human resources for collection, aggregation, and content verification. Furthermore, when outages or unauthorized access occur in infrastructure services, there has been a lack of means to quickly narrow down the affected in-house services being used, and the risk of delayed initial response has been pointed out. In addition, even during normal times, there has been a strong demand to streamline information aggregation for tasks such as regularly selecting survey targets and reporting evaluation results based on internal regulations to management.
The Role Played by the Security Assessment Platform “Assured”
To resolve the friction and the ballooning man-hours associated with such individual investigations, Assured, Inc. has developed the third-party evaluation platform “Assured Cloud Assessment.” On this platform, security experts with hands-on experience at audit firms, security consulting firms, and operating companies neutrally pre-evaluate the security measures of cloud service providers and share the resulting database among participating companies. This enables user companies to quickly access highly reliable trust evaluation information without having to conduct detailed investigations from scratch on their own. At the same time, for cloud service providers that submit information, there is a major benefit in that it reduces the burden of responding to redundant, customer-specific investigation requests. The introduction of expert-driven objective metrics contributes not only to operational efficiency for individual companies, but also to improving overall market transparency and promoting the sound utilization of digital technology.
Technical Architecture and Practical Use Cases of the Answer Search Feature
Inspection Mechanism via Question/Keyword Search and Expert Recommendations
The newly released answer search function features a technical architecture that enables the cross-sectional extraction of each vendor’s response results for specific questions from accumulated security assessment data. Specifically, by selecting the evaluation items you want to check, the responses for the target services are displayed in a list, and you can also narrow down conditions by specifying arbitrary keywords such as data center names, certification acquisition status, and expiration dates. A key feature is its ability to instantly pinpoint not only multiple-choice responses but also the detailed operational realities described in free-text fields. Additionally, an expert-driven inspection item suggestion feature has been implemented, providing search advice on the screen based on the latest attack methods and incident examples. By simply clicking the apply filters button, user companies can comprehensively inspect the services they use from multifaceted perspectives, such as understanding the data centers in use, countermeasures against unauthorized system access, account takeover prevention, contact structures, and resilience.
Practices for Rapid Response in Emergencies and Strengthening Governance in Peacetime
The use cases for this feature range widely, from initial emergency response to routine security governance operations. In the event of a crisis—such as a major outage or data breach at a cloud infrastructure provider—by searching for infrastructure usage and location information, users can identify directly affected services within minutes. Furthermore, in the event of reports regarding vulnerabilities via external services, it is possible to investigate API integrations and vendor management statuses to grasp indirect impacts through the supply chain. In daily operations, users can compare multi-factor authentication adoption rates, generative AI governance statuses, deposited data storage locations, and whether overseas access rights exist in a single view, allowing high-risk services to be singled out as priority investigation targets. Since reports summarizing third-party certification status and backup systems can be quickly generated, a rapid reporting framework for the board of directors and audit departments can be established.
Social Trends and Future Outlook of Third-Party Risk Management
The wave of regulation and standardization, such as financial guidelines and SCS evaluation systems
Currently, the social environment surrounding third-party risk management (TPRM) is at a major turning point. Especially in the financial industry, where a high level of security is required, there is a strong demand for compliance with cybersecurity guidelines for the financial sector established by the Financial Services Agency (FSA) and principles set by the international Basel Committee on Banking Supervision. In response to this, Assured Inc. released the “Assured Cloud Assessment Financial Edition,” which covers control items tailored for financial institutions, in July 2026, and it has been adopted by major institutions such as Mitsubishi UFJ Financial Group, Japan Post Bank, and Japan Exchange Group. On the administrative front as well, the Ministry of Economy, Trade and Industry (METI) is proceeding with the establishment of a cybersecurity measure evaluation system for the entire supply chain (the SCS evaluation system), aiming for operations to begin by the end of fiscal 2026. These standardization movements are increasingly functioning as a common evaluation metric in business-to-business transactions.
Future Outlook and Key Focus Areas for Cloud Risk Visualization
In future cloud security management, it is essential to move away from mere formal paper-based checks and establish a highly effective risk-based approach. By varying the depth of evaluation according to the importance of the data handled and the impact on business operations, it becomes possible to concentrate limited human resources on optimal areas. Through the distribution of evaluation information via a platform and the provision of a common metric, Assured Inc. aims to achieve the societal implementation of a security credit score that establishes a company’s security posture as an objective corporate evaluation, akin to corporate financial credit information. As cyberattacks grow more sophisticated and supply chains increasingly complex, the most critical challenge for improving society-wide cyber resilience will be to utilize not only self-help—relying on the efforts of a single company alone—but also mutual-help mechanisms that share evaluation data across the entire industry.
Reference Page
- [Cloud Service Security Credibility Assessment “Assured Cloud Assessment”] https://assured.jp/cl
- 【Assured Inc. Corporate Website】https://assured.inc
【#Cybersecurity #CloudAssessment #Assured #ThirdPartyRisk #SaaSSecurity #Visional】
コメント